Technology news and discussion on TalkFuse.
12Members
8Posts
1Active now
14,358Stories
All that stands between a hacker and admin privileges on some Linux distros is a 257-character long string of literally anything
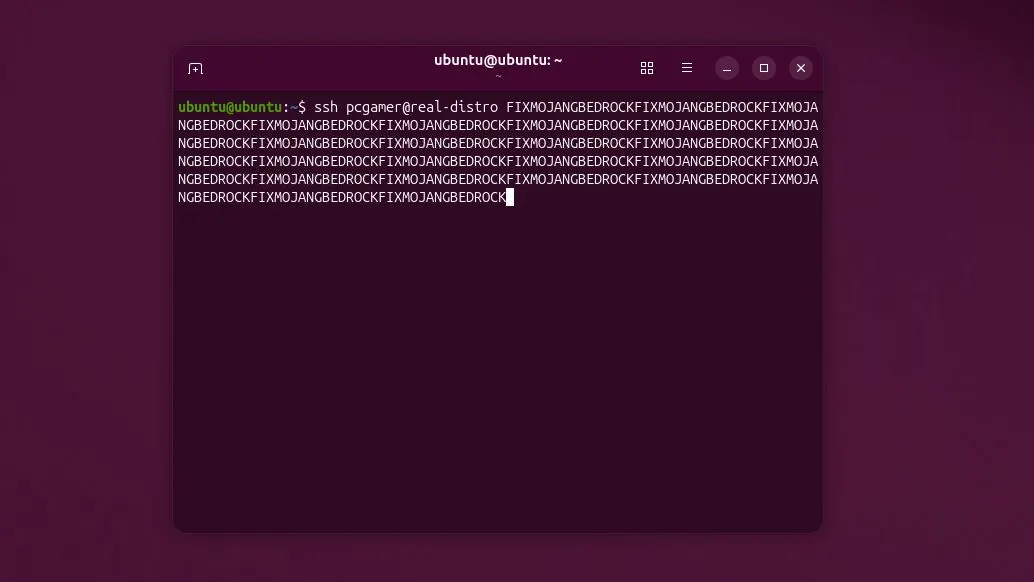
A flaw in a small number of Linux systems could let someone bypass SSH password authentication and gain root access by entering an unusually long string of characters. OpenSSH has issued a workaround, and the issue does not affect SSH generally, but it matters because SSH is widely used to manage computers remotely.
The vulnerability applies to systems using the musl C library where the SSH server runs without PAM support. The bypass involves passwords between 257 and 1,024 characters; Alpine Linux is a prominent example of a distro using musl, though it is only affected if the other conditions are met. Systems using glibc, or SSH servers with PAM enabled, are not affected according to the article.
In short
- A narrow SSH authentication flaw can grant root access.
- It affects some musl-based systems with PAM disabled.
- OpenSSH has issued a workaround.