Valve confirms CEVA breach exposed European Steam hardware customer data
Developed over time first seen 3 months ago
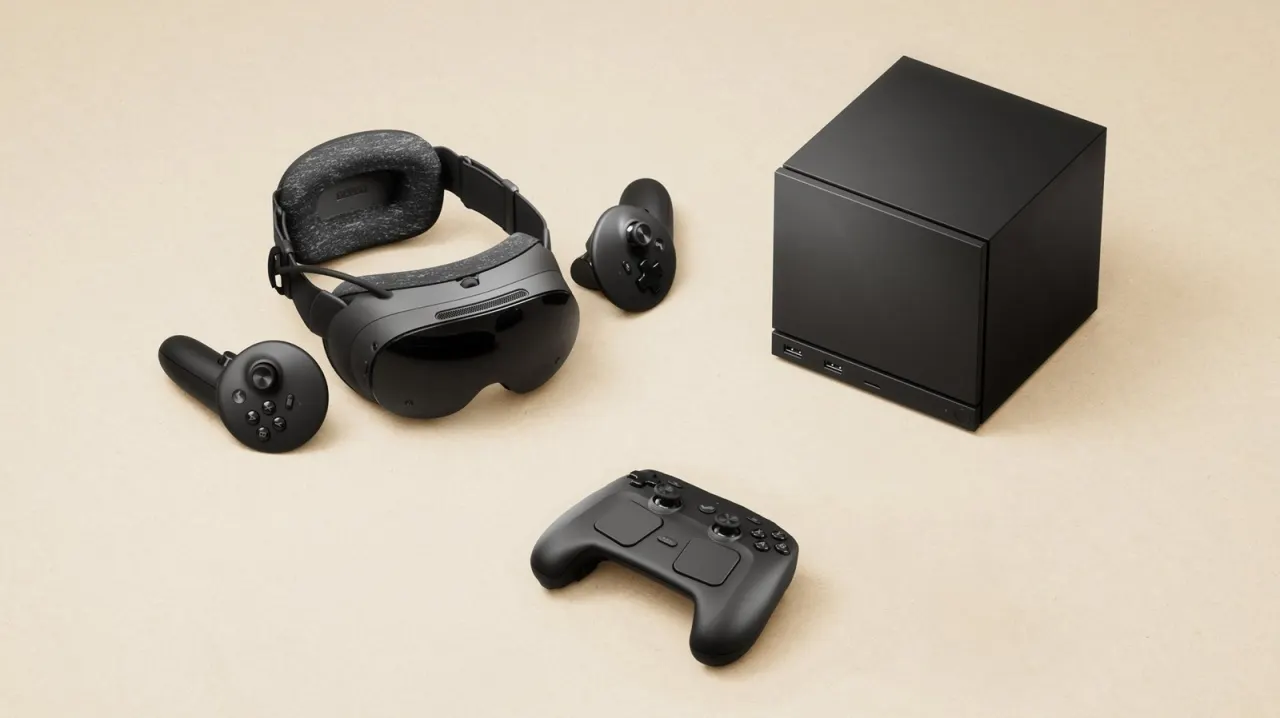
Valve has confirmed that personal data belonging to European customers who ordered Steam hardware was "likely compromised" after a cyberattack on CEVA Logistics, the firm that handles shipping for those orders. The breach matters because it leaves affected customers exposed to follow-up scams, with Valve warning that criminals may exploit the leaked details to send convincing fake messages impersonating Steam, Valve or delivery companies.
The cyberattack on CEVA Logistics took place between 29 July and 1 August, and Valve said it learned of the incident on 7 August. Stolen data includes names, addresses, phone numbers, emails and order details, but Valve confirmed that payment information, passwords and Steam Guard codes were not accessible, so affected users don't need to change their account credentials. Valve is pressing CEVA for the full scope of the breach and says it is notifying data protection authorities in the affected countries, while urging customers to be wary of unsolicited messages asking for customs or redelivery fees or account "verification".
- Sources
- 3
- Outlets
- 3
- Left · Centre · Right
- 0 · 0 · 0
In short
- CEVA Logistics breach exposed European Steam hardware customers' personal data.
- Names, addresses, phone numbers, emails and orders leaked; no payment or password data.
- Valve warns of likely follow-up phishing scams referencing hardware orders.
How this story developed
- 3 months ago Valve reiterated the same warning to affected European customers, confirming again that no payment information, passwords or Steam Guard codes were exposed, while stating it continues to push CEVA Logistics for a fuller account of how far the breach extended and is keeping national data protection regulators informed.
- 3 months ago Valve confirmed that European Steam hardware customers' personal data, including names, addresses, phone numbers, emails and order details, was likely exposed after a cyberattack on shipping partner CEVA Logistics between 29 July and 1 August, discovered on 7 August, and it urged customers to watch for phishing attempts while stressing that payment details, passwords and Steam Guard codes remained safe.
Explained simply
Valve, the company behind the digital games platform Steam, sells its own gaming hardware, such as controllers and handheld devices, to customers in Europe. Deliveries of that hardware are handled by CEVA Logistics, a shipping and logistics firm rather than a part of Valve itself, which means customer order details pass through CEVA's systems as part of the delivery process.
CEVA Logistics suffered a cyberattack, and Valve has since confirmed that personal details of its European hardware customers were caught up in the breach. This matters because the stolen information, including names, addresses and contact details, could be used by criminals to craft convincing scam messages that appear to come from Steam, Valve or a delivery company, putting affected customers at risk of follow-up fraud even though their Steam accounts and payment details were not compromised.
Coverage · 3 sources
Read the full article at the source →
Originally published by Engadget as “Data of European Steam hardware customers ‘likely compromised’, Valve says”.