Technology news and discussion on TalkFuse.
Fullerton Health server supporting migrant worker care programme hit by cybersecurity incident
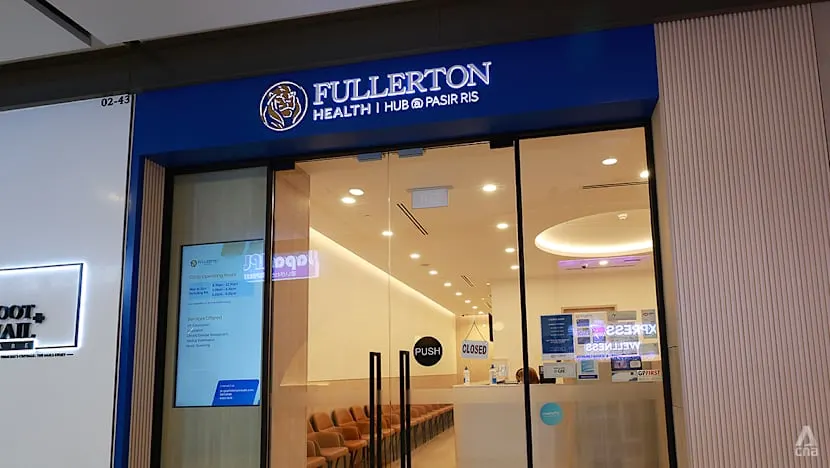
Fullerton Health said a server supporting Singapore’s Migrant Worker Primary Care Plan was accessed without authorisation, potentially exposing workers’ personal information. The incident matters because the programme serves migrant workers and is administered by the Ministry of Manpower, though the number of people affected has not been disclosed.
Preliminary findings indicate that names, foreign identification numbers, dates of birth, contact details and residential addresses may have been exposed. The company said the affected system was standalone, and it had found no evidence that health, medical or financial data, or other programmes, were affected. Fullerton Health notified the data protection regulator, police and the ministry, and is contacting potentially affected workers; investigations are continuing.
In short
- A Fullerton Health server supporting migrant worker care was accessed without authorisation.
- Several types of personal information may have been exposed.
- The number affected is unknown, and investigations continue.
Explained simply
Fullerton Health is a healthcare provider in Singapore. It runs services under the Migrant Worker Primary Care Plan, a government programme that gives migrant workers access to primary healthcare.
The Ministry of Manpower oversees the programme, while Fullerton Health supports its delivery. The personal details used to provide care can help identify and contact workers, so unauthorised access to them raises questions about privacy and how their information is protected.
Singapore’s data protection regulator oversees organisations’ handling of personal information, and police investigate potential offences. Their involvement, alongside the ministry, reflects the different responsibilities for examining the incident and supporting affected workers.
Cybersecurity Technology World