Researchers find software flaws enabling limited homebrew on Switch 2
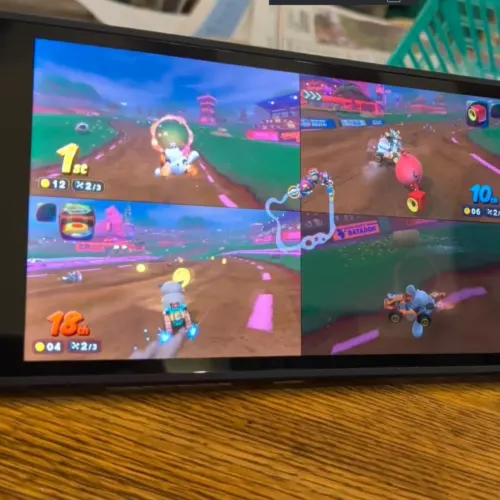
A researcher has demonstrated a software-based, partial jailbreak of Nintendo’s Switch 2, enabling homebrew software, game modifications and access to some system features. The exploit shows that hackers have found weaknesses in the console’s software, although it does not give them full control of the hardware.
The tethered method uses an integer overflow in the Switch version of SmileBasic 4, followed by a flaw in the console’s FileSystem services; it also needs a macOS or Linux computer on the same network. The researcher demonstrated modified characters in Mario Kart World, but the exploit remains limited to a userland sandbox. SmileBasic has been removed from the Switch eShop, and Nintendo may patch the vulnerability in an upcoming firmware update; the method works on firmware 23.0.1.
In short
- A software exploit gives Switch 2 hackers partial homebrew access.
- The tethered method uses flaws in SmileBasic and FileSystem services.
- It works on firmware 23.0.1 but may be patched soon.
Steelman: both sides, in good faith
The strongest fair case each way — we don't pick a winner.
The case for
Supporters of homebrew argue that owners should be able to experiment with software they run on their own consoles, customise games and use features beyond those Nintendo provides. They may see responsible disclosure of flaws as a way to improve security, while noting that this method is limited and does not grant full hardware control.
The case against
Critics argue that exploiting software flaws can undermine platform security and Nintendo’s ability to protect users, developers and the integrity of online play. Even a limited jailbreak could enable cheating or unauthorised modifications, and removing SmileBasic or patching the flaw may be justified to reduce those risks and uphold the console’s rules.
Read the full article at the source →
Originally published by Ars Technica as “Switch 2 security takes a hit as hackers unlock homebrew access”.