Australian cops cuff alleged TeamPCP masterminds
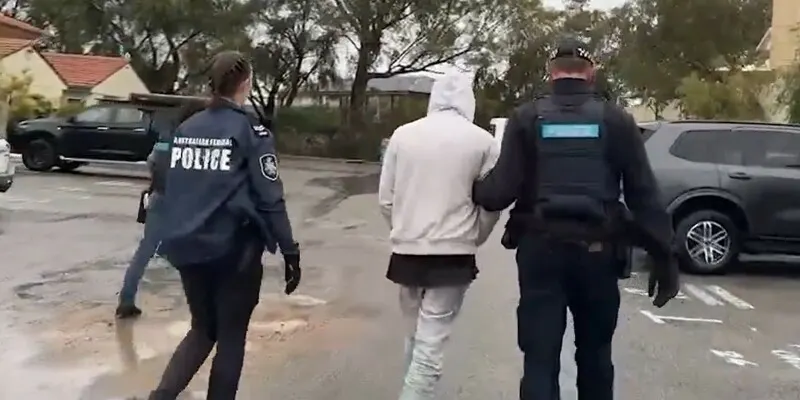
Australian Federal Police have arrested two Perth men, aged 21 and 23, accused of being principal figures in TeamPCP, a cybercrime group linked to major software supply-chain attacks. The arrests, assisted by the FBI, matter because the alleged campaigns targeted widely used open-source software and may have exposed organisations worldwide to stolen credentials, data theft and destructive malware.
The investigation began in April 2026 after threat-intelligence firms alerted Australian and US authorities to malicious code being inserted into open-source repositories. Authorities link the group to attacks including the Shai-Hulud npm worm and an earlier compromise involving the Trivy security scanner; they estimate more than 1,000 organisations may have been affected, over 500,000 credentials stolen and at least 300GB of data exfiltrated, with remediation costs potentially reaching hundreds of millions of dollars. Devices and data were seized for forensic examination, and police say further arrests or charges remain possible.
- Two Perth men were arrested over alleged TeamPCP supply-chain attacks.
- Authorities estimate over 1,000 organisations may have been compromised.
- The investigation remains ongoing, with further charges possible.
New here? Start with this
Open-source software is code that developers can inspect and use, and it often forms part of apps and services used by organisations around the world. A supply-chain attack targets this chain of tools and code, so harmful changes can spread to many users through software they trust.
TeamPCP is a cybercrime group that authorities have linked to attacks on open-source projects, including the npm package ecosystem and the Trivy security scanner. npm helps developers share JavaScript code, while Trivy is used to check software for security weaknesses.
The alleged attacks matter because compromised software can give criminals access to passwords, data or systems across many organisations. Police say the investigation involves a large number of potentially affected organisations and stolen information; the allegations have yet to be tested in court.