Business news and discussion on TalkFuse.
Google disrupts botnet infecting over 1.3 million Android TV devices
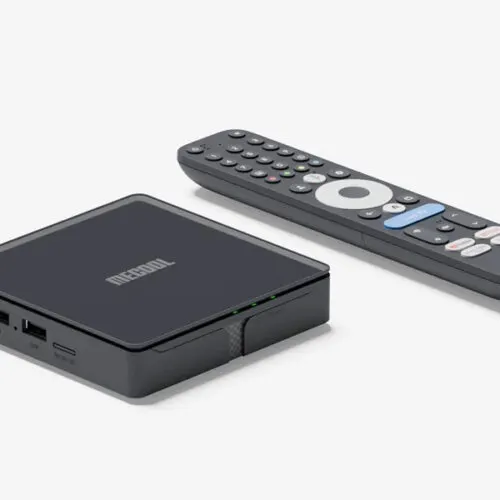
Google says it has dismantled x.cpe, a botnet that infected more than 1.3 million Google-certified Android TV devices, mainly boxes sold under the MECOOL brand. The case matters because the malware evaded Google’s certification checks and gave Videostrong Technology, the manufacturer, extensive remote access to devices and their local networks.
After the boxes were set up, a small system-level app contacted the operators, installed malware modules and disabled Play Protect. Google says the devices were used for residential proxy traffic and advertising fraud, and that access was sold to others; Trend Micro counted 1,472,554 infected devices. Google and partners disrupted the network, took legal action against its domains and servers, and barred Videostrong and its subsidiaries from Google services, while updating certification checks. The affected boxes may still have Play Protect disabled and malware modules installed, which users may find difficult to remove.
In short
- x.cpe infected more than 1.3 million Android TV devices.
- The malware disabled Play Protect and enabled remote access.
- Google cut off Videostrong and is changing certification checks.
Explained simply
Android TV is Google’s software for televisions and streaming boxes, and Google-certified devices are meant to meet its security requirements. A botnet is a group of internet-connected devices secretly controlled together; in this case, the affected boxes were mainly sold under the MECOOL brand and made by Videostrong Technology.
The software on the boxes gave Videostrong remote access to the devices and their home networks. Google says the infected boxes were used to route other people’s internet traffic and to commit advertising fraud, and that access was sold to others.
The case raises questions about how well device checks can spot hidden software and how much control manufacturers retain after sale. It also matters to owners because some affected boxes may still have harmful software or disabled security protections, which can be difficult to remove.
Business Companies Elections Entertainment Gadgets Politics Technology TV
Read the full article at the source →
Originally published by Ars Technica as “Google dismantles botnet secretly running on 1.3 million Android TV boxes”.