Business news and discussion on TalkFuse.
Pen tester used a monitor note to access company network and sensitive files
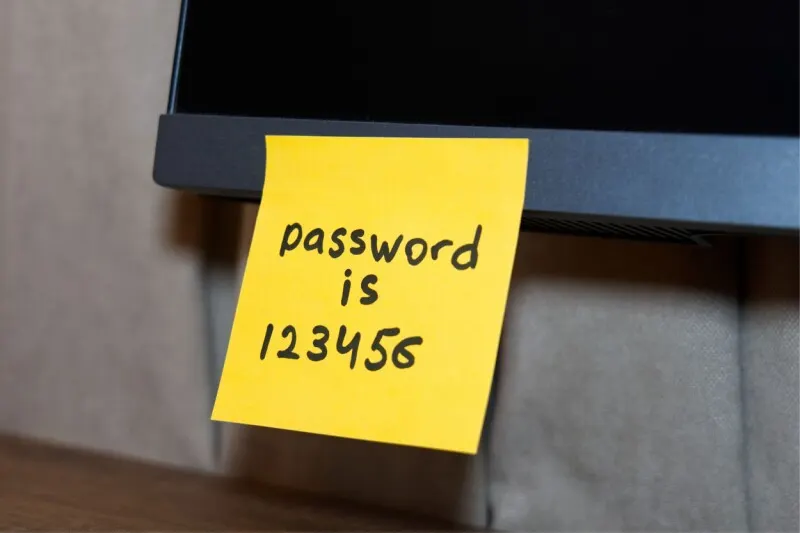
A penetration tester found a password taped to an employee’s monitor during an office walkthrough, then used it to log into the employee’s account and the company VPN. The reused credential gave him access to the company network and sensitive files, showing how a simple physical security lapse can expose data and enable fraud.
The files included employee addresses, driving licences, tax forms and salary spreadsheets, as well as server details and accounting records with vendor banking information, invoices and payments. After he reported the access, the company disabled the account, reviewed VPN logs, checked for other exposed passwords and restricted access to HR and accounting folders.
In short
- A password on a monitor unlocked the company VPN.
- Shared drives exposed employee and financial records.
- The company disabled the account and tightened file permissions.
Explained simply
A penetration tester is hired to look for weaknesses in an organisation’s systems, often by trying methods an attacker might use. A virtual private network, or VPN, lets staff connect securely to a company network from outside the office.
Passwords written down at a desk can put both an employee’s account and wider company systems at risk, especially if the same password is used for several services. HR records and accounting files can contain personal details and financial information, so access to them could create risks for employees, suppliers and the company.
Read the full article at the source →
Originally published by The Register as “Sticky note on monitor provided keys to the company’s kingdom”.